DEVSECOPS / TOOLING · 2025–2026
ScriptCCode under the microscope.
A local static analysis orchestrator. Multiple audit engines, one tool for the team.
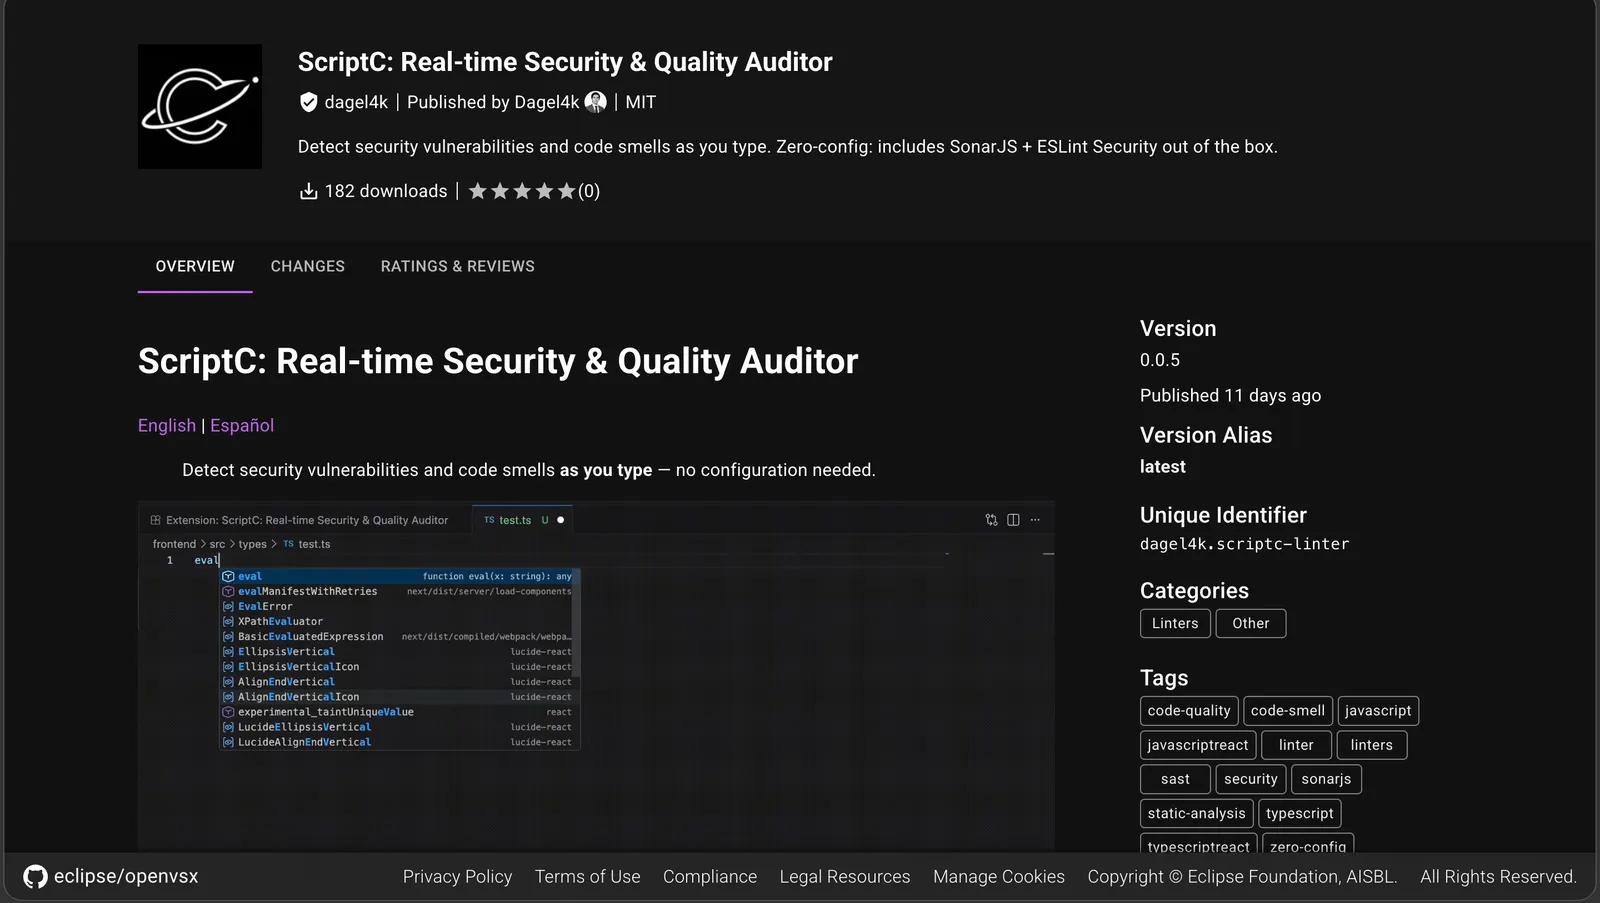
VERIFIABLE EVIDENCE · OCTOBER 2026
- Downloads on Open VSX
- 726 ↗
- Published version
- 0.0.5 · MIT license ↗
- Source code
- GitHub ↗
The problem
Reviewing quality and security with disconnected tools makes consistent standards difficult.
My contribution
Concurrent orchestration of SAST engines in isolated environments and an interface to bring their results together.
How it works
- Repository
- Isolated engines
- Concurrent analysis
- Unified report
Code analysis tool
A workflow that gathers technical review findings and makes bugs and technical debt easier to track.
The portfolio demo shows a prepared report; it does not analyze repositories or represent a real security audit.
Design decisions
- Consolidate results so code review is easier to follow.
- Keep analysis separate from the reporting interface.
I can build something like this for you
Custom software and internal tools
Web systems built around how you operate: dashboards, inventory, roles and reports.
View service →Process automation and integrations
Connect your tools and remove repetitive work: automated reports, data entry and alerts.
View service →Software QA, testing and maintenance
API testing, bug fixing and maintenance so your system does not break in production.
View service →Facing a similar problem?
We can talk through how you work today, define the scope and find a starting point.
Tell me your idea ↗